Group and privilege management
Groups are used to manage users that all need the same access and permissions to resources. For example, you can manage sudo and docker rights of users based on group membership.
Groups from the identity provider can be mapped into local Linux groups for the user. You can also configure extra groups in the broker configuration file, as described in the configuration guide.
Broker support for group management
Groups are currently supported for the msentraid broker.
Microsoft Entra ID
Microsoft Entra ID supports creating groups and adding users to them.
For example, the user authd test is a member of the Entra ID groups Azure_OIDC_Test and linux-sudo:
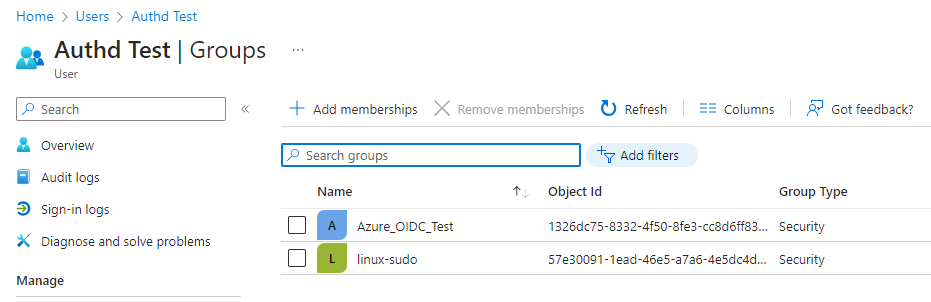
This translates to the following Linux groups on the local machine:
~$ groups
aadtest-testauthd@uaadtest.onmicrosoft.com sudo azure_oidc_test
There are three types of groups:
Primary group: Created automatically based on the user name
Local group: Group local to the machine prefixed with
linux-. For example, if the user is a member of the Azure grouplinux-sudo, they will be a member of thesudogroup locally.Remote group: All the other Azure groups the user is a member of.
Group membership resolution with Entra authentication
Group membership is read from the Microsoft Graph API. The access token obtained
from the Entra authentication flow does not carry the GroupMember.Read.All
scope, so the groups are resolved in one of two ways:
With device registration (
register_device = true): the device’s primary refresh token is exchanged for a Graph-scoped access token. No extra configuration is required.Without device registration (
register_device = false) for the Entra authentication flow: aclient_secretmust be configured in the[oidc]section. authd then uses the OIDC app’s client credentials to obtain an application-level Graph token. This requires the app registration to hold theGroupMember.Read.AllApplication permission with tenant admin consent.
If neither device registration nor a client secret is available while the Entra authentication flow is enabled, the broker fails to start because group membership cannot be resolved.